Microsoft Execution Containers become available
Microsoft Execution Containers are now generally available. Developers and IT teams can define file, network and interface boundaries that the operating environment enforces around an AI agent’s workload.
Containment sits outside the agent’s reasoning
The Microsoft release includes process containers across Windows 11, macOS and Linux, with additional backends for particular platforms. It also describes learning and permissive modes for observing access while a policy is being developed. Their behavior differs from production enforcement.
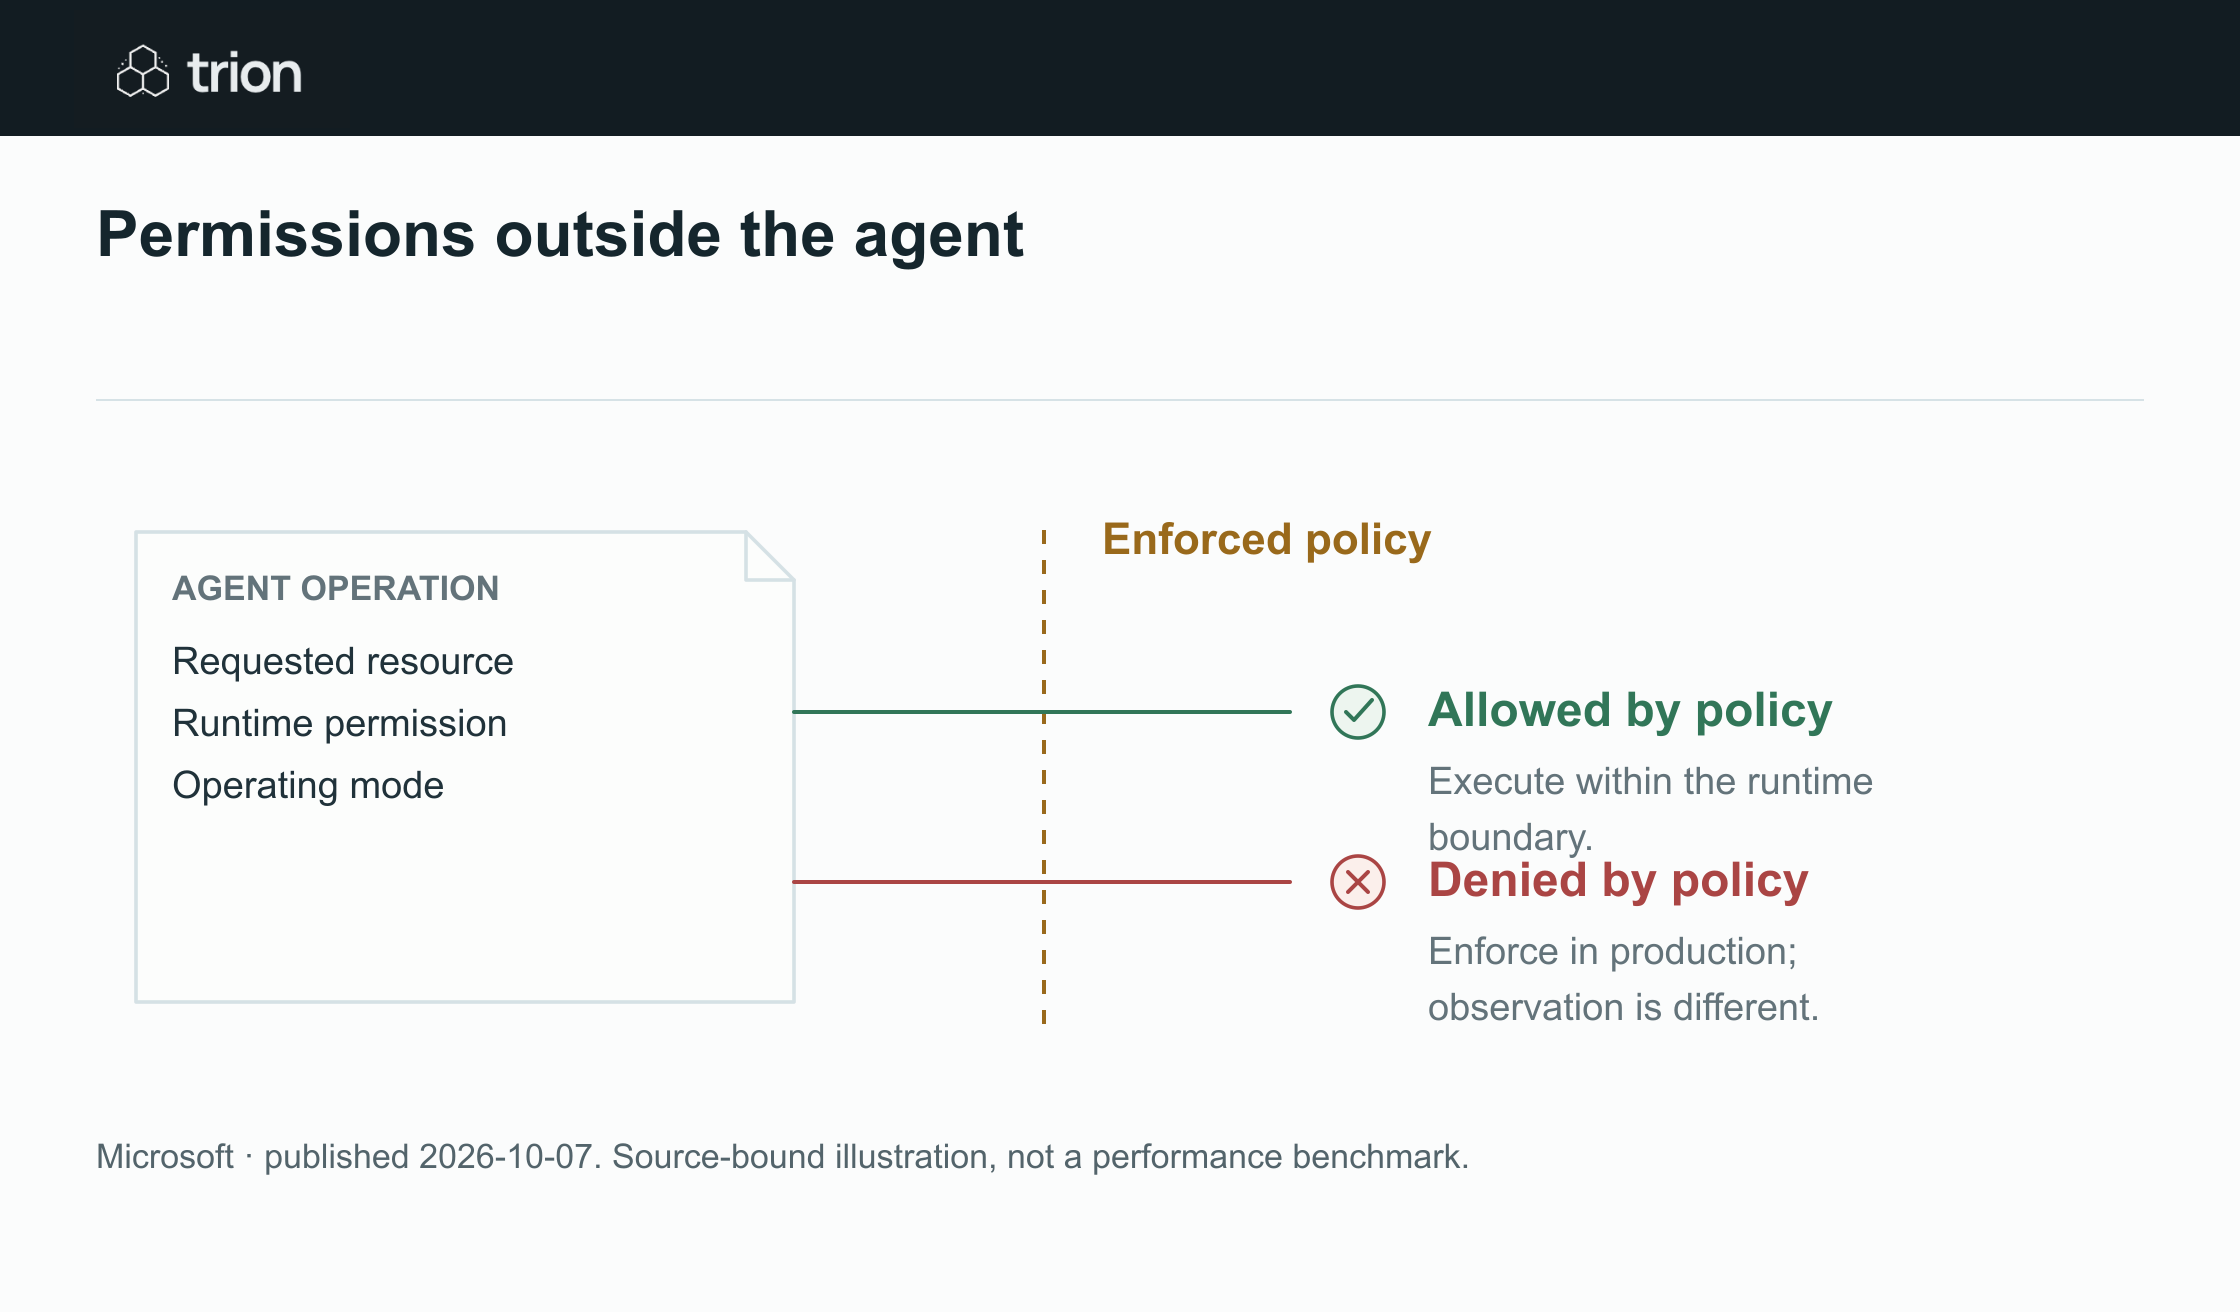
Permissions outside the agent
- Process containers
- Windows 11, macOS and Linux backends
- Learning / permissive modes
- Observe access while developing the policy
- Production enforcement
- Different from observation modes
- Entra identity and management
- Described as coming soon
View data
| Evidence | Meaning |
|---|---|
| Process containers | Windows 11, macOS and Linux backends |
| Learning / permissive modes | Observe access while developing the policy |
| Production enforcement | Different from observation modes |
| Entra identity and management | Described as coming soon |
Microsoft · published 2026-10-07. Source-bound illustration, not a performance benchmark.
Download imageAgent identity through Microsoft Entra and broader management capabilities are described as coming soon. General availability of the containment layer should therefore be separated from the future identity and administration roadmap. Backends also have different security properties.
Original sources
- Microsoft: original announcementblogs.windows.com
Checked 9 Oct 2026 · A manually curated edition. Availability may change; company performance claims are not Trion test results. Editorial method.