NVIDIA outlines security across the agent stack
NVIDIA’s new guidance treats agent security as a responsibility across the whole system. Models, tools, identities, runtime controls and logs each contribute to whether an automated action stays within its authority.
A wrong decision should meet an enforced boundary
The NVIDIA guidance uses an agent updating a customer record as an example. If malicious instructions cause it to attempt an unauthorized export, network policy should block the destination and protected logs should record the attempted action and outcome.
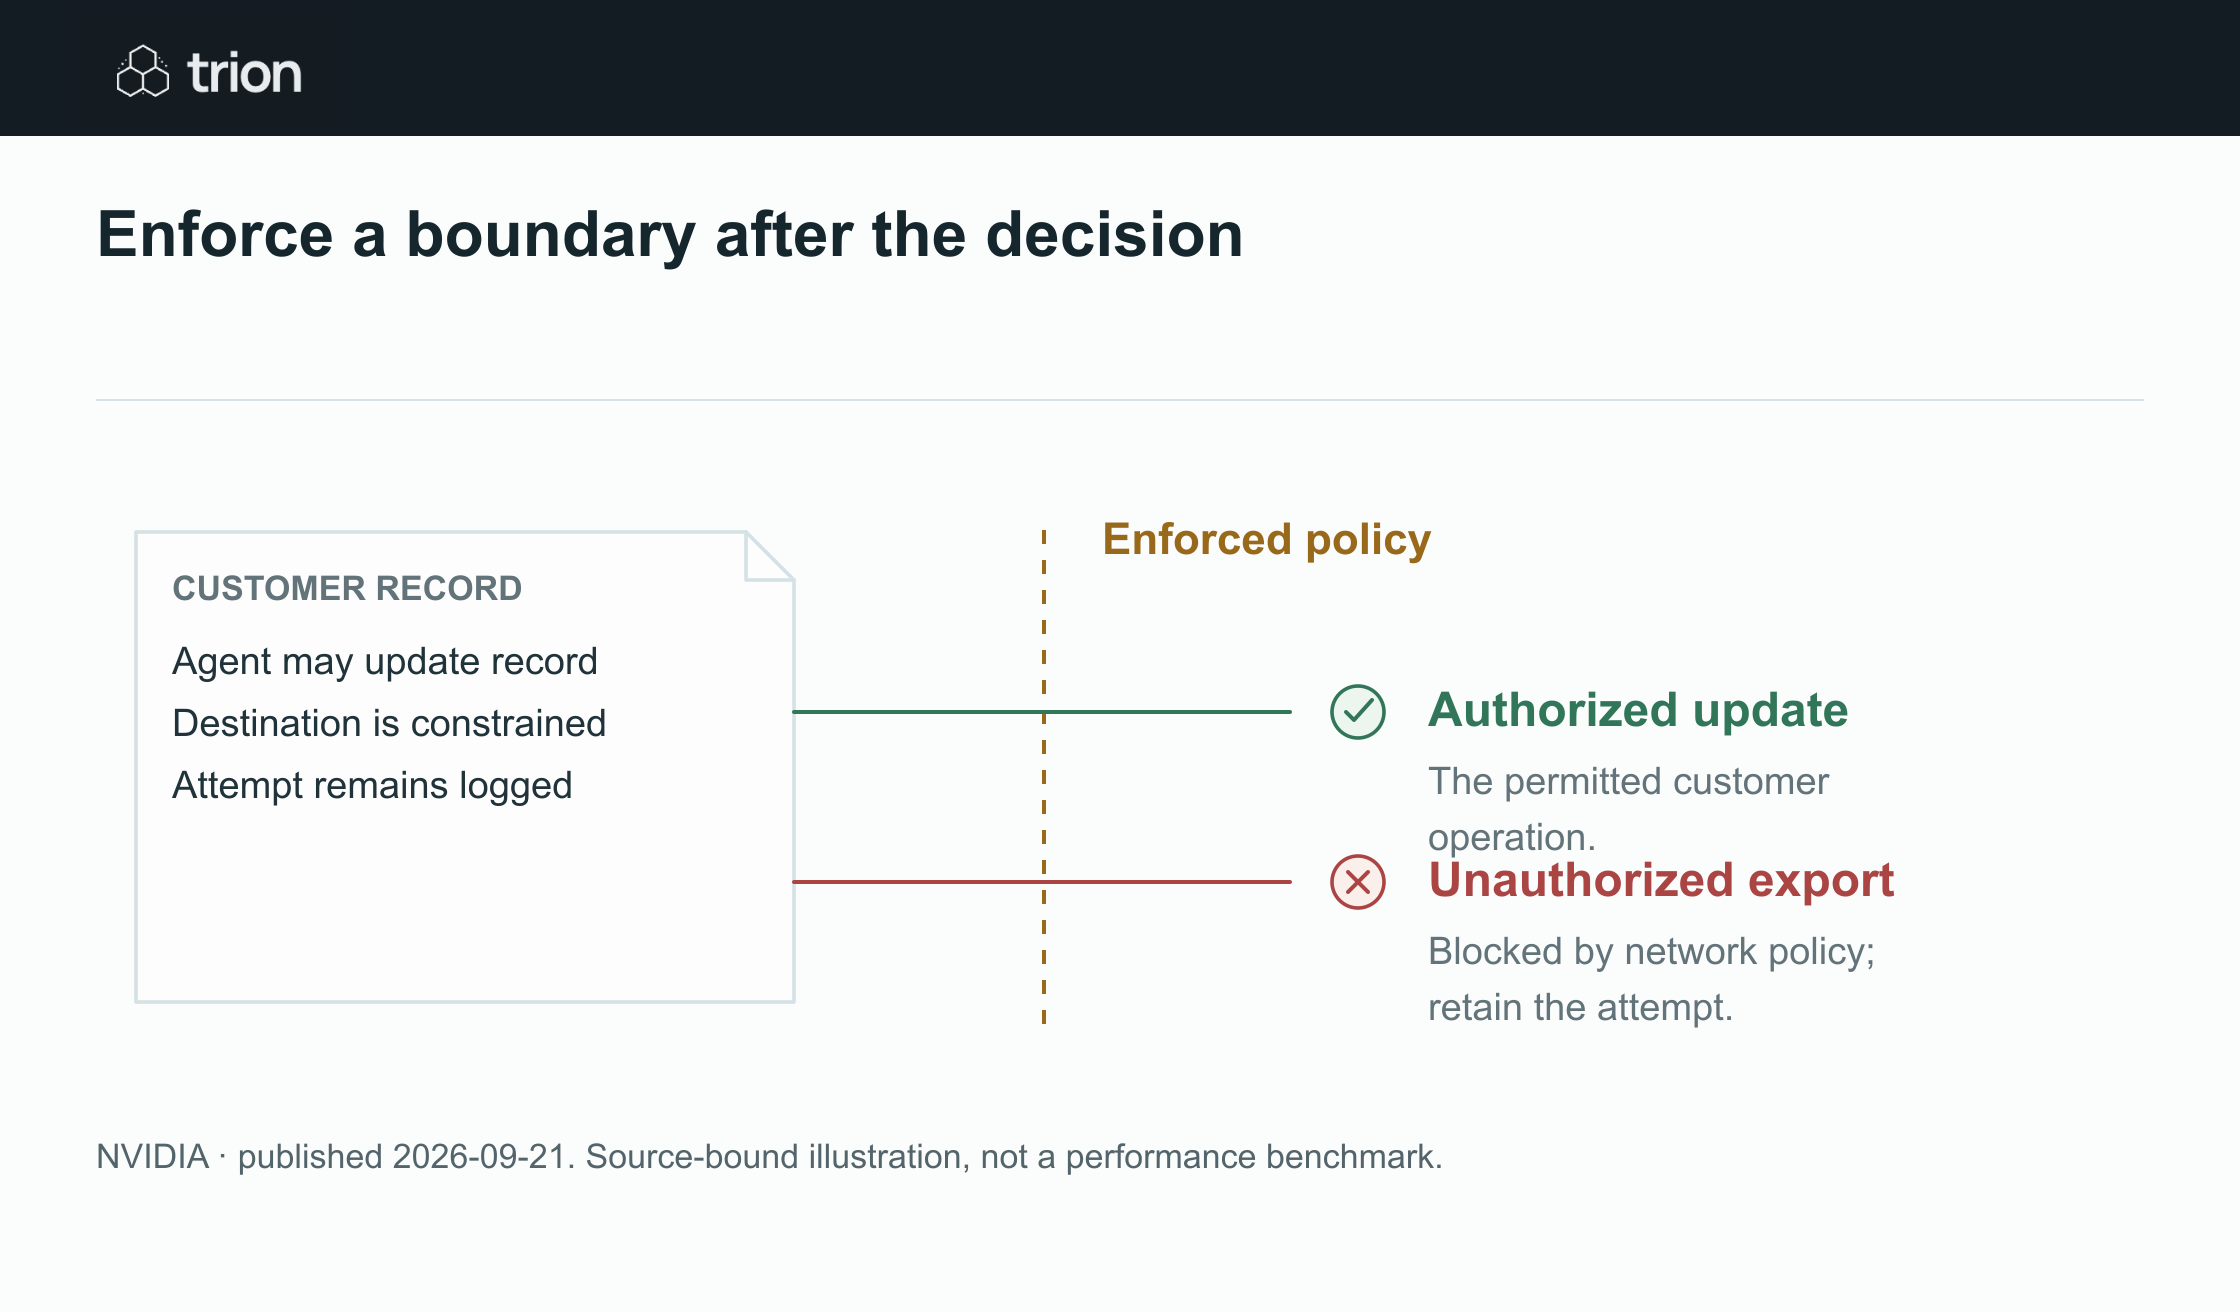
Enforce a boundary after the decision
- Update permission
- A customer record may be changed
- Export attempt
- That does not authorize data export
- Network block
- Policy blocks an unauthorized destination
- Protected log
- Record attempted action and outcome
View data
| Evidence | Meaning |
|---|---|
| Update permission | A customer record may be changed |
| Export attempt | That does not authorize data export |
| Network block | Policy blocks an unauthorized destination |
| Protected log | Record attempted action and outcome |
NVIDIA · published 2026-09-21. Source-bound illustration, not a performance benchmark.
Download imagePermission to change one record should not automatically allow exporting the data. The agent can request more access, but should not authorize that access itself. The guidance also calls for named owners, defined requirements and evidence that controls work; it is an engineering approach, not a certification for a particular application.
Original sources
- NVIDIA: original guidanceblogs.nvidia.com
Checked 9 Oct 2026 · A manually curated edition. Availability may change; company performance claims are not Trion test results. Editorial method.